
Threat Intelligence
Lateral Movement in Cybersecurity: Definition and Detection
Attackers rarely breach networks directly; they move sideways through trusted connections to reach high-value targets while staying beneath detection thresholds.
Attackers rarely breach networks directly; they move sideways through trusted connections to reach high-value targets while staying beneath detection thresholds.
Mapping blast radius reveals hidden attack paths that standard perimeter defenses miss, turning containment into a precise engineering task rather than a reactive scramble.
Distributed denial-of-service attacks succeed by exploiting network capacity limits, not by breaking encryption or stealing credentials, making traffic management the primary defense.
Profiling reveals operational habits rather than individual identities, turning noise into actionable context for detection engineering.
Enriched indicators of compromise often carry false context that degrades detection quality rather than improving operational accuracy.
Rainbow tables bypass brute-force speed limits by pre-computing hash chains, making salt the only effective countermeasure against offline credential theft.
Passkeys shift trust from memorized strings to device-bound cryptographic keys, creating new failure modes that traditional password advice ignores.
Attackers reuse captured password hashes to access systems without ever knowing the actual password or triggering standard authentication alerts.
Memory corruption occurs when programs overwrite reserved data areas, allowing attackers to hijack control flow without needing a known software flaw.
Most exposed admin panels result from misconfigured default paths and missing authentication layers rather than complex software vulnerabilities.
Website defacement is rarely a standalone theft attempt; it is a signal that an attacker has bypassed your perimeter and controls your server environment.
Small teams must prioritize architectural flaws over code bugs because a single design error in access control bypasses all downstream security controls.
Exposure management reveals hidden attack paths by correlating asset identity with real-time context, exposing risks that traditional scans miss.
Broken access control fails when servers trust client-side inputs to determine user permissions, allowing attackers to bypass intended boundaries without exploiting code logic errors.
A botnet remains active because it uses decentralized communication channels that bypass traditional perimeter defenses and survive device resets.
Small organizations often pay for shared infrastructure without realizing that weak tenant separation exposes them to data leakage from unrelated customers.
Treating vulnerability management as a simple scanning task ignores the complex operational reality of asset discovery and risk context.
Hybrid warfare blends technical intrusions with narrative manipulation, requiring analysts to track information flow rather than just network traffic to identify true intent.
Self-hosted GitLab flaws often stem from complex integration points where standard web defenses fail to inspect internal application logic.
Most small firms fail because they ignore data classification, turning minor credential leaks into reportable regulatory events.
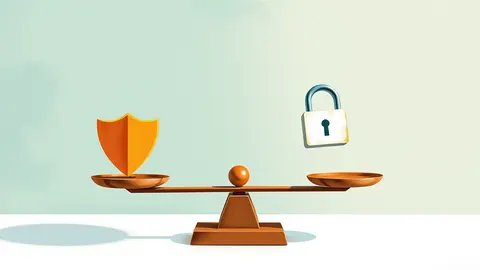
Most security programs fail because they optimize for confidentiality while ignoring the hidden costs of enforcing data integrity and system availability.
Identity theft insurance shifts the financial burden of forensic investigation and legal defense from your operating budget to a predetermined risk pool.
Input validation fails when teams treat it as a front-end feature rather than a backend constraint, leaving the core logic exposed to malformed data.
CAPTCHA creates friction that blocks automated abuse but simultaneously pushes attackers toward more expensive manual labor or sophisticated bot networks.