Threat Intelligence
Recorded Future Links TAG-193 to Central Asian Espionage Campaigns
Researchers document state-linked intrusions targeting diplomatic and resource sectors across CIS nations through phishing and code hosting.
Threat Intelligence coverage from NetSec Tribune holds 21 articles, 19 of them reference guides. The newest was published on October 15, 2026. New stories are added as soon as they are confirmed, from more than 150 sources checked as often as every 45 seconds. Each story lists its sources. Primary sources we follow for this section include CISA Cybersecurity Advisories and FIRST: Forum of Incident Response and Security Teams.
Researchers document state-linked intrusions targeting diplomatic and resource sectors across CIS nations through phishing and code hosting.
Disabling pre-authentication on a single account creates a permanent offline cracking vector that survives password rotation and remains undetected by standard login alerts.

Attackers rarely breach networks directly; they move sideways through trusted connections to reach high-value targets while staying beneath detection thresholds.
Profiling reveals operational habits rather than individual identities, turning noise into actionable context for detection engineering.
Enriched indicators of compromise often carry false context that degrades detection quality rather than improving operational accuracy.
Attackers reuse captured password hashes to access systems without ever knowing the actual password or triggering standard authentication alerts.
Hybrid warfare blends technical intrusions with narrative manipulation, requiring analysts to track information flow rather than just network traffic to identify true intent.
A single domain triggered 40 billion passive DNS records in days, expanding across over 100 domains during military operations, according to GBHackers.
Raw packet data reveals protocol anomalies that endpoint logs miss, but storing unfiltered traffic creates storage debt and privacy liabilities that scale faster than your detection capabilities.
Credential theft in small networks often bypasses login screens entirely by stealing stored authentication tokens rather than guessing passwords.
Treating indicators as absolute proof of compromise ignores the high false-positive rate inherent in static data without behavioral context.
The framework maps adversary behavior to specific techniques, allowing you to build detection logic that survives tool changes and obfuscation efforts.
Static domain blocking fails against domain generation algorithms, requiring defenders to deploy sinkhole infrastructure and monitor algorithmic patterns instead.
Raw feed data degrades detection accuracy unless you map each indicator to a specific attack technique and validate it against your current asset inventory.
Restricting process access rights removes the majority of credential theft risk without requiring complex application changes or constant monitoring.
Strategic intelligence converts raw telemetry into resource allocation decisions, revealing that most teams waste budget on data they cannot act upon.
Domain generation algorithms do not create random noise; they produce deterministic strings that allow defenders to predict and sinkhole malicious infrastructure before execution.
Default Sysmon settings log routine noise while ignoring the specific binary behaviors that indicate an active compromise, requiring manual tuning to surface true threats.
The Cyber Kill Chain stops at initial compromise, while MITRE ATT&CK maps the entire post-breach lifecycle, revealing lateral movement and data exfiltration paths that earlier models ignore.
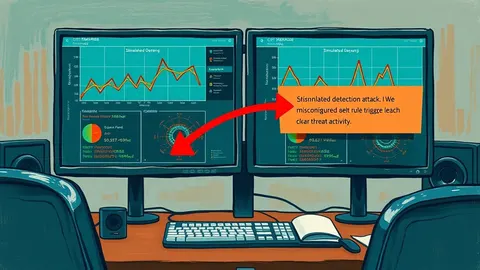
Purple teaming exposes detection failures faster than red teaming, but it often reveals that your monitoring tools are configured incorrectly rather than missing.
The framework separates adversary intent from specific tools, allowing you to detect new malware using existing behavioral logic.