
Cloud Security
Cloud Metadata Service Attacks: Response and Recovery Steps
Automated scripts harvest cloud credentials within seconds of exposure, forcing responders to isolate instances before rotating keys to prevent lateral movement.
Cloud Security coverage from NetSec Tribune holds 18 articles, 16 of them reference guides. The newest was published on October 14, 2026. New stories are added as soon as they are confirmed, from more than 150 sources checked as often as every 45 seconds. Each story lists its sources. Primary sources we follow for this section include NIST Cybersecurity Framework and Cloud Security Alliance.
Automated scripts harvest cloud credentials within seconds of exposure, forcing responders to isolate instances before rotating keys to prevent lateral movement.
Serverless architecture shifts the attack surface from infrastructure to configuration and data, rendering traditional perimeter defenses obsolete.
Logging records discrete events for forensic analysis, while monitoring aggregates metrics to trigger automated responses in real time.
Small organizations often pay for shared infrastructure without realizing that weak tenant separation exposes them to data leakage from unrelated customers.
Physical drone strikes on facilities in Sasovo, Kaluga and Vladimir forced Yandex to shut down services and recommend customers activate backup plans.
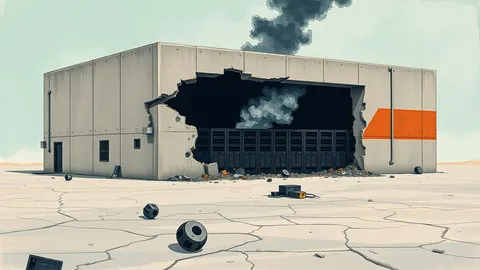
A Ukrainian drone attack on a Yandex facility in Vladimir caused widespread outages for cloud, AI, and consumer apps across Russia on Sunday.
Default SaaS settings and weak identity policies create silent entry points that attackers exploit long before any network perimeter is breached.
Most container failures stem from silent defaults that grant excessive permissions, turning minor oversights into systemic risks.
CIS Benchmarks provide a consensus-driven configuration baseline that reduces your cloud attack surface by hardening default settings.
Admission controllers act as a gatekeeper that validates and mutates requests before objects are persisted to the cluster storage layer, preventing misconfigurations from ever becoming reality.
Most cloud penetration tests fail because they treat infrastructure like traditional servers, ignoring the unique attack surface of APIs and identity services.
Small teams can secure cloud environments by automating detection and delegating complex forensics, avoiding the trap of manual log analysis that drains limited staff time.
Misconfigured policies often grant more access than intended, turning zero trust into a complex permission system that fails during incident response.
Orphaned resources often remain active and billable long after their owning application is deleted, creating silent security gaps that standard cleanup scripts miss.
The cloud attack surface shifts from network perimeters to identity and configuration, making traditional perimeter defenses ineffective against modern threats.
Rotating access keys reduces the window of compromise but often fails to stop attacks that exploit permissions or configuration errors rather than stolen credentials.
Role-based access control restricts API server requests, preventing lateral movement when a container workload is compromised by an attacker.
Most container security fails because teams secure the recipe but leave the kitchen doors unlocked for anyone to cook with.