
Vulnerabilities
Bug Bounty Triage Explained: How to Filter Noise From Real Threats
Most reported vulnerabilities are false positives or low-impact issues that require minimal effort to dismiss, saving teams from wasting resources on noise.
Reference guides from the NetSec Tribune newsroom. They explain the ideas behind the headlines and are reviewed when the facts change.
Most reported vulnerabilities are false positives or low-impact issues that require minimal effort to dismiss, saving teams from wasting resources on noise.

Compensating controls shift risk rather than eliminate it, requiring continuous validation to prevent security posture decay over time.

An accurate asset inventory reveals hidden endpoints that bypass security controls, ensuring patches reach every system before threat actors exploit known vulnerabilities.
Browser zero-days rarely require direct user interaction; automated exploit chains and internal network traversal make passive exposure the primary risk vector for modern web clients.
Pre-authentication flaws bypass access controls entirely, allowing attackers to execute code or extract data without any valid credentials or session tokens.
Publicly accessible .git directories allow attackers to reconstruct your entire source code history, bypassing standard access controls and revealing sensitive credentials.
Patch prioritization replaces vulnerability counts with risk context, ensuring teams fix the issues that attackers can actually exploit before they run out of time or resources.
Broken build logs and unexpected artifact hashes reveal compromise long before application code is inspected for flaws or misconfigurations.
WebSocket connections bypass traditional web security controls, allowing attackers to exploit authenticated sessions with minimal detection overhead.
Workflow injection risks extend beyond public pull requests into trusted internal code, static analysis gaps, and the complex interaction of environment variable parsing rules.
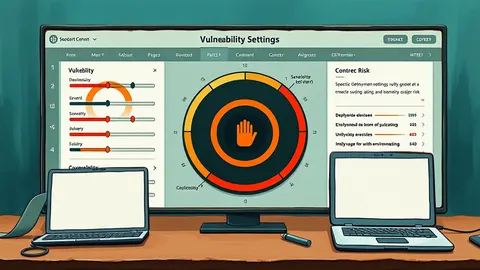
CVSS environmental scores adjust base severity ratings by factoring in specific deployment conditions, revealing risks that generic vulnerability databases consistently overlook.

Automated scripts harvest cloud credentials within seconds of exposure, forcing responders to isolate instances before rotating keys to prevent lateral movement.
Spyware degrades system performance and leaks credentials before any ransom demand appears, creating a persistent blind spot in standard security monitoring.
Physical paper remains a primary vector for data exfiltration because standard digital controls fail to track or protect information once it leaves the screen.
Serverless architecture shifts the attack surface from infrastructure to configuration and data, rendering traditional perimeter defenses obsolete.

Rapid network isolation prevents lateral movement, but preserving forensic evidence requires leaving compromised systems powered on during the initial containment phase.
Logging records discrete events for forensic analysis, while monitoring aggregates metrics to trigger automated responses in real time.
Most remote access trojans hide in plain sight by mimicking legitimate system processes and using standard administrative tools to avoid detection.
Software restriction policies fail when teams treat them as static lists rather than dynamic controls that require constant validation against changing application dependencies.
Ransom notes are cryptographic receipts that prove encryption occurred, but they rarely contain the decryption key or reliable contact information for recovery.

Botnets hide in plain sight by using legitimate device connections to mask malicious traffic from standard network monitoring tools.
Most logging systems capture noise rather than signal, leaving teams blind to lateral movement and silent data exfiltration during active incidents.
Disabling pre-authentication on a single account creates a permanent offline cracking vector that survives password rotation and remains undetected by standard login alerts.
Most bot protection fails because it treats all automation as hostile, blocking legitimate tools while malicious scripts slip through behavioral gaps.