Data Breaches
Printed Document Leak Myths: What Security Teams Get Wrong
Physical paper remains a primary vector for data exfiltration because standard digital controls fail to track or protect information once it leaves the screen.
Data Breaches coverage from NetSec Tribune holds 16 articles, 16 of them reference guides. The newest was published on October 14, 2026. New stories are added as soon as they are confirmed, from more than 150 sources checked as often as every 45 seconds. Each story lists its sources. Primary sources we follow for this section include NIST Cybersecurity Framework and UK Information Commissioner's Office.
Physical paper remains a primary vector for data exfiltration because standard digital controls fail to track or protect information once it leaves the screen.

Rapid network isolation prevents lateral movement, but preserving forensic evidence requires leaving compromised systems powered on during the initial containment phase.
Most logging systems capture noise rather than signal, leaving teams blind to lateral movement and silent data exfiltration during active incidents.
Most small firms fail because they ignore data classification, turning minor credential leaks into reportable regulatory events.
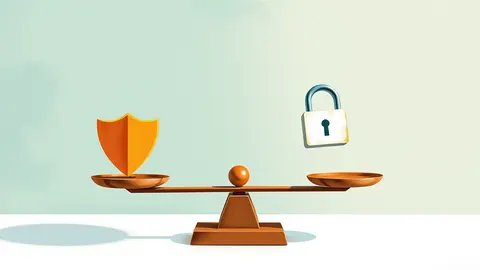
Most security programs fail because they optimize for confidentiality while ignoring the hidden costs of enforcing data integrity and system availability.
Identity theft insurance shifts the financial burden of forensic investigation and legal defense from your operating budget to a predetermined risk pool.
Data masking replaces real values with fictional substitutes that preserve format and functionality while removing the ability to reconstruct original sensitive records.
A pre-written communication plan reduces response time but cannot prevent technical failure or stop data from leaving your network.
Encryption at rest protects data on storage media but offers zero protection if an attacker gains valid access credentials or if the decryption keys are compromised.
Full disk encryption renders stolen hardware useless by scrambling data into unreadable noise without the cryptographic key.
Data exfiltration often succeeds not through complex hacking, but by exploiting legitimate channels that security tools are configured to ignore or trust.
Attackers rarely bypass authentication; they usually operate with legitimate credentials that your standard monitoring tools are configured to ignore.
Credential dumps allow attackers to bypass perimeter defenses by using stolen login data, turning weak authentication into full system compromise.
A credit freeze blocks new account openings entirely, while a fraud alert merely adds a verification step that criminals can often bypass with stolen identity data.
Assigning permissions to roles rather than individuals prevents privilege creep and simplifies access management when employees change jobs or leave the organization.
Encrypting email subjects prevents metadata leaks that reveal business intent, even when the message body remains secret.