Data Breaches
Audit Logging Misconceptions: 6 Ways Teams Fail at Evidence
Most logging systems capture noise rather than signal, leaving teams blind to lateral movement and silent data exfiltration during active incidents.
Everything NetSec Tribune has reported about security operations: 6 stories, newest first. Part of our Threat Intelligence coverage.
Most logging systems capture noise rather than signal, leaving teams blind to lateral movement and silent data exfiltration during active incidents.
Enriched indicators of compromise often carry false context that degrades detection quality rather than improving operational accuracy.
Most data loss originates from authorized accounts that bypass perimeter defenses, making internal behavior harder to detect than external attacks.
Treating indicators as absolute proof of compromise ignores the high false-positive rate inherent in static data without behavioral context.
Raw feed data degrades detection accuracy unless you map each indicator to a specific attack technique and validate it against your current asset inventory.
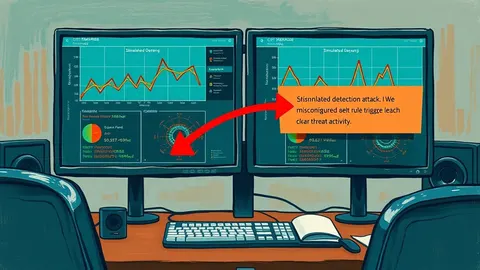
Purple teaming exposes detection failures faster than red teaming, but it often reveals that your monitoring tools are configured incorrectly rather than missing.