Threat Intelligence
Threat Actor Profiling: 6 Common Misreadings and Correct Views
Profiling reveals operational habits rather than individual identities, turning noise into actionable context for detection engineering.
Everything NetSec Tribune has reported about threat intelligence: 8 stories, newest first. Part of our Threat Intelligence coverage.
Profiling reveals operational habits rather than individual identities, turning noise into actionable context for detection engineering.
Enriched indicators of compromise often carry false context that degrades detection quality rather than improving operational accuracy.
Hybrid warfare blends technical intrusions with narrative manipulation, requiring analysts to track information flow rather than just network traffic to identify true intent.
Treating indicators as absolute proof of compromise ignores the high false-positive rate inherent in static data without behavioral context.
The framework maps adversary behavior to specific techniques, allowing you to build detection logic that survives tool changes and obfuscation efforts.
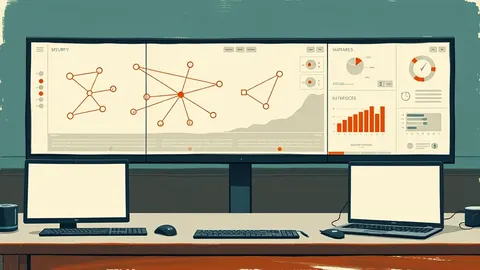
Raw feed data degrades detection accuracy unless you map each indicator to a specific attack technique and validate it against your current asset inventory.
Domain generation algorithms do not create random noise; they produce deterministic strings that allow defenders to predict and sinkhole malicious infrastructure before execution.
The framework separates adversary intent from specific tools, allowing you to detect new malware using existing behavioral logic.