Cyber Attacks
Stop Session Hijacking: Low-Cost Defenses for Small Teams
Session cookies are often the only key attackers need, making token binding and strict domain policies more effective than complex firewalls for small teams.
Session cookies are often the only key attackers need, making token binding and strict domain policies more effective than complex firewalls for small teams.
Crypto-stealers bypass traditional defenses by mapping the file system for wallet data rather than exploiting cryptographic keys directly, turning local storage into the primary attack surface.
Domain generation algorithms do not create random noise; they produce deterministic strings that allow defenders to predict and sinkhole malicious infrastructure before execution.
Defacement is often the visible tip of a larger compromise where the attacker already controls your server processes and database connections.
Tamper protection shifts security from user-level discretion to kernel-enforced immutability, blocking administrative overrides that malware exploits.
Default Sysmon settings log routine noise while ignoring the specific binary behaviors that indicate an active compromise, requiring manual tuning to surface true threats.
Malicious packages often hide in transitive dependencies, meaning your direct code is clean while the supply chain delivers the compromise.
The Cyber Kill Chain stops at initial compromise, while MITRE ATT&CK maps the entire post-breach lifecycle, revealing lateral movement and data exfiltration paths that earlier models ignore.
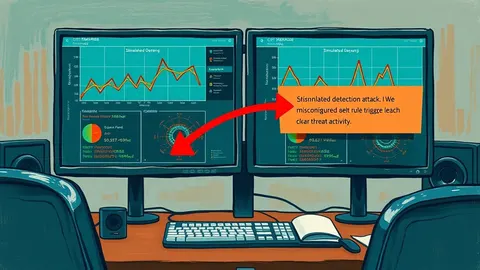
Purple teaming exposes detection failures faster than red teaming, but it often reveals that your monitoring tools are configured incorrectly rather than missing.
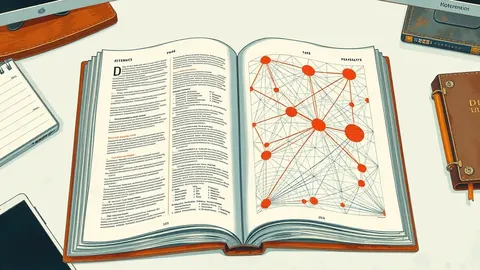
The framework separates adversary intent from specific tools, allowing you to detect new malware using existing behavioral logic.
Most sandbox evasion techniques exploit the predictable behavior of automated analysis environments rather than breaking cryptographic protections or hiding from human analysts.
Assigning permissions to roles rather than individuals prevents privilege creep and simplifies access management when employees change jobs or leave the organization.
Most container security fails because teams secure the recipe but leave the kitchen doors unlocked for anyone to cook with.
Encrypting email subjects prevents metadata leaks that reveal business intent, even when the message body remains secret.
See how authorization failures allow unauthorized data access and how to architect defenses that enforce least privilege at every layer.
Identify why default settings fail, how to automate verification, and where human error bypasses your strongest encryption layers.